- Security researcher HD Moore, chief research officer at Dragos, seeded roughly 2 million unique tracking secrets into prompts sent through AI routers like OpenRouter and Vercel to test for data leakage.
- The experiment found at least three AI providers were compromised by attackers who stole the secrets directly from incoming prompts.
- Several resellers in the AI inference marketplace logged prompts and passed stolen credentials to third parties despite “Zero Data Retention” settings.
- One Chinese AI lab’s systems fetched secret URLs embedded in more than half of prompts sent to its models between July and October, including roughly two-thirds marked as no-data-collection.
What Happened
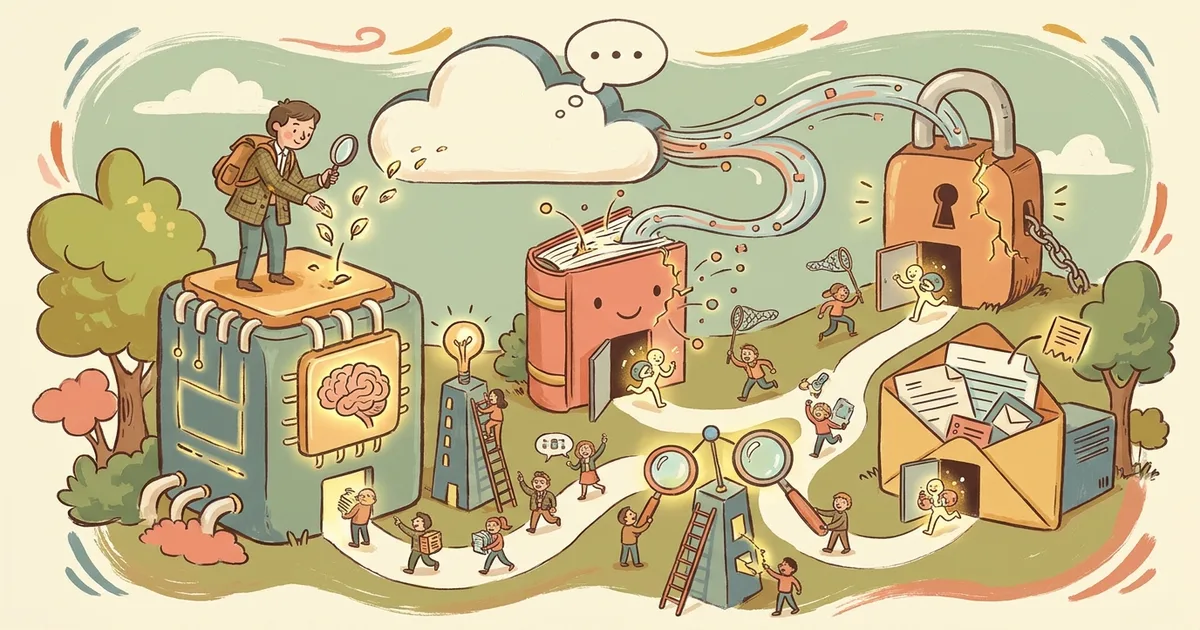
Security researcher HD Moore seeded nearly 2 million unique secrets, including AWS access keys and private URLs, into prompts routed through AI gateways such as OpenRouter and Vercel, then tracked where those secrets resurfaced, according to Ars Technica (Nov 20, 2026). Moore wrote that the test “revealed security breaches, prompt theft, and widespread failures to protect customer data.”
Why It Matters
The findings echo earlier supply-chain failures in the AI tooling ecosystem, including the LiteLLM gateway breach that exposed roughly 97 million MCP installs and LiteLLM’s own split from a controversial data partner. They suggest privacy flags like Zero Data Retention don’t survive contact with a multi-hop reseller network.
Technical Details
Attackers compromised three separate hosting providers and reused “a couple hundred” stolen AWS keys within hours of each canary being seeded, using them tens of thousands of times to probe S3 buckets and secrets managers. In two of the three breaches, some of the stolen requests were marked Zero Data Retention. Secrets sent to two of the hacked providers were used together almost immediately from the same rented server, pointing to a single attacker behind both.
Who’s Affected
Developers who route AI traffic through third-party inference brokers to cut costs are most exposed, since prompts are decrypted at every hop in the chain. Enterprises that picked a specific hosting region to keep data onshore were also affected, Moore found, after one lab routed scraped URLs back overseas regardless of which US reseller handled the request.
What’s Next
Moore recommends self-hosting models or contracting directly with a single first-tier provider rather than default reseller pools, though he notes neither approach guarantees secrets stay private.